Cyber threats are becoming more sophisticated, persistent, and difficult to detect. Organizations today operate across cloud platforms, remote work environments, enterprise networks, SaaS applications, data centers, and interconnected business systems. Every connection creates potential opportunities for cybercriminals to exploit vulnerabilities, steal sensitive information, disrupt operations, or gain unauthorized access.
Traditional cybersecurity tools such as firewalls, antivirus software, and endpoint protection solutions remain important, but they are not sufficient on their own. Organizations need a coordinated approach that continuously monitors security events, identifies suspicious activity, investigates potential incidents, and responds before threats cause significant damage.
This is where a Security Operations Center (SOC) becomes essential.
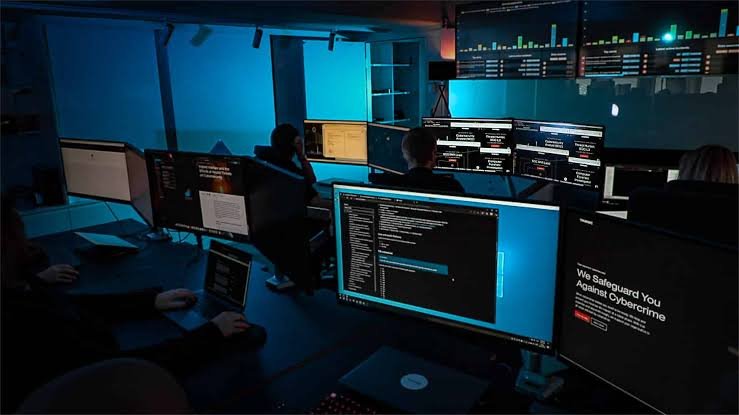
A Security Operations Center is a centralized function responsible for monitoring, detecting, analyzing, and responding to cybersecurity threats across an organization’s IT environment. It combines security professionals, processes, and technologies to provide continuous visibility into potential risks and coordinate incident response activities.
Whether an organization operates a small IT environment or a complex multi-cloud infrastructure, an effective SOC helps reduce security blind spots, improve threat detection, and strengthen overall cyber resilience.
What Is a Security Operations Center (SOC)?
A Security Operations Center is a dedicated security team or operational function that monitors an organization’s systems, networks, applications, endpoints, and cloud environments to identify and respond to cybersecurity threats.
The primary objective of a SOC is to detect suspicious activity as early as possible and coordinate an appropriate response before an incident escalates.
A SOC typically performs several interconnected activities:
- Continuous security monitoring across enterprise environments.
- Collection and analysis of security logs and event data.
- Detection of suspicious behavior and potential cyberattacks.
- Investigation and prioritization of security alerts.
- Incident containment, remediation, and recovery coordination.
- Threat intelligence analysis and proactive threat hunting.
- Security reporting, compliance support, and continuous improvement.
For example, consider an employee account that suddenly attempts to access sensitive financial records from an unusual location after several failed login attempts. A SOC can correlate authentication logs, endpoint activity, network connections, and identity information to determine whether the activity represents a potential account compromise.
If the activity is confirmed as malicious, the SOC can coordinate actions such as disabling the compromised account, revoking active sessions, isolating affected devices, and investigating whether sensitive information was accessed.
Without centralized security monitoring, these events may remain unnoticed until suspicious activity develops into a larger incident.
Why Organizations Need a Security Operations Center
Cybersecurity threats are no longer limited to isolated malware infections or unauthorized network access. Modern attacks can involve phishing, ransomware, credential theft, supply chain compromises, cloud misconfigurations, insider threats, and exploitation of software vulnerabilities.
Several factors make SOC capabilities increasingly important.
1. Increasing Complexity of IT Infrastructure
Organizations use multiple technology environments, including on-premises servers, public cloud platforms, private clouds, SaaS applications, and remote endpoints.
Each environment generates security events and requires appropriate monitoring. When security information is scattered across disconnected tools, identifying relationships between events becomes difficult.
A SOC brings relevant security information together to improve visibility across the organization’s technology environment.
2. Advanced and Persistent Cyber Threats
Attackers increasingly use techniques designed to remain undetected for extended periods.
They may steal legitimate credentials, move between systems, abuse administrative privileges, or use trusted applications to execute malicious activities.
A SOC can correlate seemingly unrelated events to identify suspicious patterns that individual security tools might miss.
3. Faster Incident Detection and Response
The longer an attacker remains undetected, the greater the potential damage.
Security operations teams continuously monitor alerts and investigate suspicious activity to reduce the time between an initial compromise and an effective response.
Faster detection can help limit data exposure, operational disruption, and recovery costs.
4. Regulatory and Compliance Requirements
Organizations operating in regulated industries must often demonstrate that they maintain appropriate security monitoring, incident management, access controls, and risk management practices.
A SOC can support these activities by maintaining security records, documenting incidents, monitoring control effectiveness, and coordinating investigations.
Applicable requirements depend on the organization’s industry, location, data, and regulatory obligations.
5. Growing Insider Threat Risks
Not every security incident originates outside an organization. Employees, contractors, and compromised internal accounts can also introduce security risks.
A SOC can monitor unusual access patterns, unexpected privilege changes, suspicious file transfers, and other activities that may indicate insider threats or account compromise.
Monitoring should be proportionate, transparent, and governed by appropriate employee privacy and access policies.
How a Security Operations Center Works
A SOC operates through a continuous cycle of collecting security information, identifying potential threats, investigating alerts, responding to incidents, and improving security controls.
Its effectiveness depends on the integration of people, processes, and technology.
1. Security Data Collection
The first stage involves collecting security information from different parts of the IT environment.
Typical sources include:
- Firewalls and network security devices.
- Servers and operating systems.
- Endpoint detection and response tools.
- Identity and access management systems.
- Cloud infrastructure and SaaS applications.
- Email security platforms.
- Web application firewalls.
- Database activity monitoring systems.
These systems generate logs and telemetry that help security analysts understand what is happening across the organization.
2. Security Event Correlation
Collected information is analyzed to identify relationships between individual events.
For example, a failed login attempt may not be suspicious by itself. However, multiple failed attempts followed by a successful login, privilege escalation, and unusual data access could indicate a compromised account.
Security Information and Event Management (SIEM) platforms help aggregate, normalize, correlate, and analyze security events from multiple sources.
3. Threat Detection and Alert Prioritization
Detection systems identify activities that match known attack patterns, suspicious behaviors, or predefined security rules.
Alerts may be generated for activities such as:
- Malware detection.
- Unauthorized privilege escalation.
- Suspicious authentication attempts.
- Unusual outbound network traffic.
- Access to restricted information.
- Unexpected changes to security configurations.
SOC analysts evaluate these alerts based on severity, business impact, confidence, and potential threat activity.
4. Incident Investigation
When an alert requires further attention, analysts investigate the underlying activity.
They may examine authentication records, endpoint telemetry, network traffic, file activity, threat intelligence, and historical security events.
The goal is to determine whether the alert represents a genuine security incident, understand its scope, and identify the systems or accounts involved.
5. Incident Response and Containment
Once a threat is confirmed, the SOC coordinates appropriate containment and remediation activities.
Depending on the incident, actions may include isolating an endpoint, disabling compromised credentials, blocking malicious network connections, removing malware, or restricting access to affected systems.
Major incidents may require coordination with IT infrastructure, cloud engineering, legal, compliance, communications, and business leadership teams.
6. Recovery and Continuous Improvement
After containment, affected systems are restored according to approved recovery procedures.
The SOC also conducts post-incident reviews to understand how the incident occurred, which controls failed, and what improvements are required.
Lessons learned can lead to stronger detection rules, better access controls, improved employee awareness, and updated incident response procedures.
Key Functions of a Modern SOC
An effective SOC performs several functions that work together to strengthen an organization’s cybersecurity posture.
Continuous Security Monitoring
Continuous monitoring provides visibility into security activity across enterprise systems.
SOC analysts monitor incoming alerts, review suspicious events, and identify abnormal behavior that could indicate a cyberattack.
For organizations operating around the clock, monitoring may be provided through internal shifts, outsourced services, or a hybrid operating model.
Threat Intelligence
Threat intelligence provides information about potential attackers, malicious infrastructure, vulnerabilities, and known attack techniques.
SOC teams use intelligence from trusted sources to improve detection rules and understand emerging threats.
For example, if threat intelligence identifies infrastructure associated with a phishing campaign, the SOC can check whether enterprise systems have communicated with those indicators.
Threat intelligence is most valuable when it is relevant to the organization’s technology environment and integrated into operational security workflows.
Threat Hunting
Threat hunting is a proactive security activity in which analysts investigate environments for suspicious activity that may not have generated an alert.
Instead of waiting for security tools to identify a known threat, analysts develop hypotheses based on attacker behavior and search for supporting evidence.
For example, a threat hunter may investigate whether privileged accounts are accessing systems at unusual times, whether endpoints are executing unexpected administrative tools, or whether suspicious authentication patterns indicate lateral movement.
Threat hunting helps identify potential threats that automated detection systems may overlook.
Vulnerability Management
SOC teams often work closely with vulnerability management and IT infrastructure teams to understand exposure to known security weaknesses.
This may involve reviewing vulnerability alerts, monitoring exploitation attempts, prioritizing critical findings, and verifying whether affected systems have been remediated.
The SOC does not necessarily own vulnerability remediation, but it plays an important role in identifying active threats and communicating security priorities.
Incident Response Management
Incident response is one of the most critical SOC responsibilities.
A well-defined incident response process establishes how security incidents are detected, classified, investigated, contained, eradicated, and recovered from.
The NIST Cybersecurity Framework provides a useful reference for organizing cybersecurity risk management activities, while the NIST incident response guidance helps organizations develop structured response capabilities.
Essential Technologies Used in a Security Operations Center
Modern SOCs depend on multiple security technologies to collect information, detect threats, investigate incidents, and automate response activities.
| Technology | Primary Function | SOC Use Case |
|---|---|---|
| SIEM | Centralized security event management | Correlating logs and identifying suspicious activity |
| EDR | Endpoint detection and response | Detecting malware and unusual endpoint behavior |
| XDR | Extended detection and response | Correlating security activity across multiple environments |
| SOAR | Security orchestration, automation, and response | Automating repetitive investigation and response tasks |
| IDS/IPS | Intrusion detection and prevention | Identifying or blocking suspicious network activity |
| Threat Intelligence Platform | Threat data aggregation and analysis | Enriching alerts with information about known threats |
| Vulnerability Management | Identifying and prioritizing weaknesses | Monitoring exposure and remediation progress |
| UEBA | User and entity behavior analytics | Identifying unusual account or system behavior |
| NDR | Network detection and response | Detecting suspicious network communication and lateral movement |
| CSPM | Cloud security posture management | Identifying cloud configuration risks and security weaknesses |
These technologies serve different purposes and should be integrated based on the organization’s threat landscape, infrastructure, operational maturity, and budget.
A larger security toolset does not automatically create a more effective SOC. Proper configuration, data quality, integration, and skilled analysis are equally important.
Understanding SIEM, SOAR, EDR, and XDR in SOC Operations
Four technologies are particularly important in modern security operations: SIEM, SOAR, EDR, and XDR.
Security Information and Event Management (SIEM)
SIEM platforms collect and analyze security events from different systems.
They help analysts identify suspicious activity by correlating information from multiple sources.
For example, a SIEM system may correlate unusual login activity, access to sensitive files, and unexpected network connections to generate a high-priority alert.
Security Orchestration, Automation, and Response (SOAR)
SOAR platforms automate repetitive security workflows and coordinate actions across different security tools.
For example, when a phishing email is confirmed as malicious, an automated workflow may search for similar messages, remove them from mailboxes where supported, collect relevant indicators, and notify the security team.
Automation reduces manual effort and allows analysts to focus on complex investigations.
Endpoint Detection and Response (EDR)
EDR solutions monitor endpoint activity and provide visibility into suspicious processes, file behavior, network connections, and other endpoint events.
If an endpoint shows signs of ransomware activity, EDR capabilities may help security teams investigate the behavior and isolate the affected device.
Extended Detection and Response (XDR)
XDR extends detection and response across multiple security domains, potentially combining endpoint, network, identity, email, and cloud telemetry.
By correlating information across these environments, XDR can help analysts investigate threats that span multiple systems.
Although SIEM, SOAR, EDR, and XDR may overlap in certain capabilities, they are not interchangeable. A mature SOC uses them according to its operational requirements and technology architecture.
How SOCs Detect and Prevent Common Cyber Threats
A SOC supports the detection and containment of different cyber threats by combining security monitoring, threat intelligence, behavioral analysis, and incident response.
1. Phishing and Business Email Compromise
Phishing attacks attempt to trick employees into sharing credentials, opening malicious attachments, or transferring money to fraudulent accounts.
Business email compromise attacks may involve compromised accounts or impersonation of trusted business contacts.
SOC teams monitor email security alerts, suspicious authentication activity, malicious links, unusual mailbox rules, and abnormal communication patterns.
If an account is compromised, the SOC can coordinate credential resets, session revocation, mailbox investigation, and containment measures.
2. Ransomware Attacks
Ransomware can encrypt business information, disrupt critical systems, and create significant operational damage.
SOC teams monitor suspicious file modifications, abnormal process execution, unusual encryption behavior, and unexpected connections to external infrastructure.
Early detection can help isolate affected endpoints, restrict malicious activity, and protect unaffected systems.
Organizations should also maintain tested backups and recovery plans because detection alone cannot guarantee that ransomware damage will be prevented.
3. Insider Threats
Insider threats may involve malicious actions by employees or contractors, but they can also result from compromised internal accounts or accidental data exposure.
SOC analysts investigate unusual access to sensitive information, unexpected downloads, suspicious privilege changes, and abnormal data transfers.
Effective insider threat monitoring requires coordination with HR, legal, compliance, and data protection teams, with clear controls to protect employee privacy.
4. Distributed Denial-of-Service (DDoS) Attacks
DDoS attacks attempt to overwhelm online services by generating excessive traffic from multiple sources.
SOC teams monitor traffic patterns, network availability, unusual request volumes, and service performance indicators.
They may coordinate with network providers, cloud security teams, and DDoS mitigation services to filter malicious traffic and maintain service availability.
5. Unauthorized Access and Credential Theft
Attackers frequently exploit stolen passwords, weak authentication mechanisms, and excessive privileges to access enterprise systems.
SOC teams monitor unusual login locations, repeated authentication failures, suspicious session behavior, unexpected privilege changes, and abnormal access patterns.
Integration with identity and access management systems helps security teams investigate potential account compromise more effectively.
6. Cloud Security Threats
Cloud environments introduce risks such as exposed storage, excessive permissions, compromised access keys, and unauthorized configuration changes.
A SOC can monitor cloud audit logs, identity activity, network connections, and configuration alerts to identify potential security incidents.
Cloud security monitoring should cover relevant infrastructure, platform services, SaaS applications, and identity systems rather than focusing exclusively on virtual machines.
SOC Operating Models: In-House, Managed, and Hybrid
Organizations can establish SOC capabilities through different operating models depending on their size, security requirements, available expertise, and financial resources.
In-House SOC
An in-house SOC is operated by an organization’s internal security team.
The organization manages its security personnel, tools, processes, and monitoring infrastructure.
Advantages:
- Greater direct control over security operations.
- Strong understanding of internal business systems.
- Customizable monitoring and response procedures.
- Direct coordination with internal IT and leadership teams.
Challenges:
- Higher staffing and technology costs.
- Difficulty recruiting and retaining experienced analysts.
- Challenges in maintaining continuous coverage.
- Ongoing investment in tools, training, and infrastructure.
Managed Security Operations Center
A Managed Security Operations Center is operated by an external security service provider.
The provider supplies monitoring capabilities, security analysts, detection technologies, and incident support under an agreed service arrangement.
Advantages:
- Access to specialized security expertise.
- Reduced requirement to build a complete internal SOC.
- Potentially faster deployment.
- Flexible monitoring and service options.
Challenges:
- Dependence on an external provider.
- Need for clear service-level agreements.
- Data-sharing and privacy considerations.
- Potential limitations in understanding internal business context.
Hybrid SOC
A hybrid SOC combines internal security personnel with external security services.
For example, an organization may retain internal ownership of incident management and security strategy while outsourcing continuous monitoring and selected investigation activities.
This model can balance operational control with access to specialized capabilities.
| Operating Model | Best Suited For | Main Consideration |
|---|---|---|
| In-house SOC | Organizations with mature security teams and complex requirements | Staffing and operating costs |
| Managed SOC | Organizations seeking external security expertise | Provider quality and service accountability |
| Hybrid SOC | Organizations combining internal oversight with external support | Clear ownership and coordination |
There is no universally correct operating model. Organizations should select one based on risk exposure, business requirements, regulatory obligations, and available resources.
The Role of AI and Automation in Modern SOCs
Security operations teams face a growing volume of alerts, logs, and threat intelligence. Investigating every alert manually can overwhelm analysts and delay incident response.
Artificial intelligence and automation are helping SOC teams improve operational efficiency.
AI-Powered Threat Detection
Machine learning models can analyze patterns in network traffic, endpoint behavior, and authentication activity to identify unusual events.
For example, a system may detect that an employee account is accessing applications and resources in a way that differs significantly from its normal activity.
Such anomalies can help analysts identify potential threats, although unusual behavior does not automatically indicate malicious activity.
Automated Alert Prioritization
AI-assisted systems can help classify alerts according to severity, confidence, asset importance, and available threat context.
This can reduce the time analysts spend reviewing low-priority events and help them focus on incidents that require immediate attention.
Automated Incident Response
SOAR workflows can execute approved response actions when specific conditions are met.
Examples include:
- Disabling or restricting compromised accounts.
- Isolating affected endpoints.
- Blocking confirmed malicious indicators.
- Collecting evidence from security tools.
- Creating incident tickets.
- Notifying relevant response teams.
High-impact actions should have appropriate approval requirements, safeguards, and rollback procedures.
Generative AI for Security Analysts
Generative AI can help analysts summarize security alerts, explain unfamiliar log entries, draft incident reports, and retrieve relevant investigation procedures.
However, organizations must carefully govern the use of AI in security operations. Sensitive logs, credentials, customer information, and incident evidence should not be submitted to unauthorized external services.
AI-generated conclusions must also be validated by qualified analysts before major response decisions are made.
AI should support security professionals rather than replace human judgment and accountability.
Key SOC Performance Metrics Every Organization Should Track
A SOC needs measurable performance indicators to understand how effectively it detects, investigates, and responds to security threats.
Some of the most useful metrics include:
| SOC Metric | What It Measures | Why It Matters |
|---|---|---|
| Mean Time to Detect (MTTD) | Average time taken to identify a security incident | Measures detection effectiveness |
| Mean Time to Respond (MTTR) | Time taken to respond to an incident; organizations should define the exact response milestone | Measures response speed |
| Mean Time to Contain | Time required to contain a confirmed threat | Indicates how quickly incident impact is limited |
| Alert False Positive Rate | Proportion of alerts incorrectly classified as threats | Helps evaluate detection quality |
| Incident Resolution Time | Time taken to resolve security incidents | Measures overall incident handling efficiency |
| Security Coverage | Visibility across relevant systems and assets | Identifies monitoring gaps |
| Threat Detection Coverage | Coverage of relevant threat techniques and behaviors | Helps identify detection weaknesses |
| Automation Rate | Proportion of eligible workflows handled automatically | Measures operational efficiency |
Metrics should be interpreted together. A low MTTD is valuable, but it does not guarantee effective security if alerts are poorly prioritized or incidents remain unresolved.
Similarly, a high automation rate is not necessarily positive if automated workflows produce incorrect or disruptive actions.
SOC performance should ultimately reflect improved risk reduction, incident handling, and business resilience.
How to Build an Effective Security Operations Center
Establishing a SOC requires careful planning, appropriate technology, skilled personnel, and well-defined operating procedures.
Organizations should begin with their security requirements rather than purchasing multiple tools without a clear operational strategy.
Step 1: Assess the Security Environment
Identify critical business systems, sensitive information, cloud platforms, network infrastructure, endpoints, and major security risks.
Determine which assets require continuous monitoring and which regulatory or contractual requirements influence SOC operations.
Step 2: Define the SOC Operating Model
Decide whether the SOC will be operated internally, through a managed provider, or through a hybrid arrangement.
Define ownership of monitoring, investigations, incident response, escalation, and reporting.
Step 3: Select Appropriate Security Technologies
Choose SIEM, EDR, XDR, SOAR, threat intelligence, and other security technologies according to actual business requirements.
Prioritize integration and visibility over unnecessary tool expansion.
Step 4: Establish Security Processes
Develop standard operating procedures for alert investigation, incident classification, escalation, evidence preservation, containment, recovery, and post-incident reviews.
Create clear communication channels between security, IT, legal, compliance, and business teams.
Step 5: Build the SOC Team
Depending on the operating model, relevant roles may include SOC analysts, incident responders, threat hunters, detection engineers, security engineers, and SOC managers.
Provide continuous training on emerging threats, investigation methods, security tools, and incident response procedures.
Step 6: Implement Monitoring and Detection
Connect relevant systems to the monitoring environment and establish detection rules for high-priority threats.
Validate that logs are complete, reliable, properly timestamped, and retained according to organizational requirements.
Step 7: Test Incident Response Capabilities
Conduct tabletop exercises, attack simulations, and controlled security tests to evaluate whether the SOC can detect and respond to realistic incidents.
Use the results to improve detection logic, response procedures, and communication processes.
Step 8: Measure and Improve
Review SOC metrics, incident outcomes, alert quality, monitoring coverage, and operational costs.
Regularly update security processes to reflect changes in the organization’s infrastructure and threat landscape.
Common Challenges in SOC Operations
Even organizations with advanced security technologies can struggle to operate an effective SOC.
Alert Fatigue
Large volumes of low-quality alerts can overwhelm analysts and make it difficult to identify genuine threats.
Organizations should improve detection rules, enrich alerts with relevant context, and prioritize incidents based on business risk.
Shortage of Skilled Security Professionals
Cybersecurity requires specialized knowledge across networks, cloud platforms, identity systems, endpoint security, and incident response.
Organizations should invest in training, structured career development, knowledge sharing, and appropriate external support.
Tool Integration Problems
Disconnected security products can create visibility gaps and duplicate alerts.
A well-designed security architecture should establish reliable data integration and clear workflows across relevant platforms.
Incomplete Log Visibility
A SOC cannot effectively investigate events that are not recorded or accessible.
Organizations should identify critical log sources, validate data collection, and establish appropriate retention and access policies.
Unclear Incident Ownership
Security incidents often involve multiple departments. Without clearly defined responsibilities, response actions may be delayed.
Incident response plans should identify decision-makers, escalation paths, communication responsibilities, and approval requirements.
The Future of Security Operations Centers
The SOC is evolving from a primarily reactive monitoring function into a more proactive, intelligence-driven, and automated security operation.
Several developments are likely to shape its future.
AI-assisted security operations: AI will increasingly support alert triage, investigation summaries, threat correlation, and response recommendations.
Extended detection and response: Organizations will continue integrating endpoint, network, identity, email, and cloud security information to improve threat visibility.
Cloud-native security monitoring: As enterprises expand their use of cloud services, SOC capabilities will need to address dynamic infrastructure, distributed identities, containers, and cloud-native applications.
Proactive threat hunting: Security teams will increasingly investigate attacker behaviors and potential weaknesses before confirmed incidents occur.
Identity-focused threat detection: Stolen credentials and identity compromise will remain major concerns, making identity telemetry and access monitoring essential SOC capabilities.
Security automation and agentic AI: More advanced systems may coordinate multi-step investigations and approved response workflows. However, organizations will need strong human oversight, access controls, auditability, and safeguards against incorrect actions.
The future SOC will not simply generate more alerts. It will need to identify meaningful threats faster, make better decisions, and coordinate effective responses with less operational friction.
Frequently Asked Questions (FAQs) –
The primary purpose of a SOC is to monitor an organization’s IT environment, detect cybersecurity threats, investigate suspicious activities, and coordinate incident response to reduce security risks and business disruption.
A Network Operations Center (NOC) focuses primarily on network availability, performance, and infrastructure operations. A Security Operations Center focuses on cybersecurity threats, security monitoring, incident investigation, and response. Both teams may collaborate when security incidents affect network availability or business services.
Common SOC technologies include SIEM, SOAR, EDR, XDR, IDS/IPS, threat intelligence platforms, vulnerability management tools, UEBA, and network detection and response solutions.
Conclusion
Cyber threats continue to evolve, and organizations need more than individual security tools to protect their digital environments. They need a coordinated security function that can monitor activity, identify suspicious behavior, investigate incidents, and respond effectively.
A Security Operations Center provides this capability by bringing together security professionals, processes, and technologies. Through continuous monitoring, threat intelligence, proactive threat hunting, incident response, and automation, SOCs help organizations improve visibility and reduce the potential impact of cyberattacks.
However, building an effective SOC is not simply about deploying SIEM platforms or hiring security analysts. Success depends on clear operating procedures, reliable security data, skilled professionals, appropriate technology integration, and continuous improvement.
As organizations adopt AI, cloud computing, remote work, and increasingly interconnected business systems, SOC capabilities will become an important part of enterprise cyber resilience.
Ultimately, an effective SOC does more than detect threats. It helps organizations respond with confidence, protect critical assets, maintain business continuity, and build a stronger foundation for digital trust.
The 4th Vision
Independent insight on AI, data, cloud and technology strategy, written to help leaders understand what comes next and act on it.